

SEC-Line PLATFORM
SEC-Line PLATFORM
Catalog excerpts
Using Embedded Computers in Edge Computing Kontron Open Platform for Far Edge Micro Clouds ► Turnkey firewall / router with OEMU™ hypervisor for any OS support ► Security by design: hardware root of trust, secure boot and measured boot ► Small footprint (<200 MByte) distribution with cyber-attacks self protection ► Remote fleet management with OpCenter supports remote attestations ► Deploy and protect in a single computer unmodified software from multiple boxPC
Open the catalog to page 1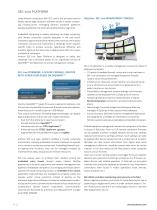
Using Kontron computers with SEC-Line is the quickest route to deploy secure edge computer software stacks in todays’ computing infrastructures, leveraging Kontron hardware platforms already qualified for the most demanding industry segments. Embedded computing is rapidly morphing into Edge computing, with always connected systems deployed in the real world. Exposed to logical and physical attacks, they must be continuously monitored, secured and maintained, a challenge which requires specific tools to achieve security, operational efficiency and business agility at the same time in deployments...
Open the catalog to page 2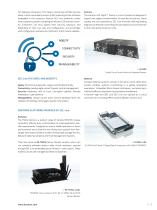
For deployed computers, this means monitoring certified sources about critical vulnerability events (CVE) impacting all the software embedded in the computer. Kontron SEC-Line platforms comes with a quarterly bulletin compiling all relevant CVE and their severity. Customers can thus assess their security exposure, and depending on their use case and configuration, act accordingly with configuration workaround, hotfixes or full firmware updates. Avionics The Kontron ACE Flight™ family is a line of products designed to support the digital transformation of commercial avionics. Some models are now...
Open the catalog to page 3
► TPM-based Secure Boot prevents device refactoring ► Secrets protection : all passwords, encryption keys and certificates are protected by the TPM ► Measured boot using TPM hashing mechanism enables Remote attestation ► Approtect™ protects application software also in Virtual Machines ► Control of device networking (wired, wireless, LTE, VPN) ► Settings management: local via a GUI, remote via OpCenter ► Health monitoring engine, a single view of the system in the CBIT dashboard ► File Access Control: AppArmor restricts software to known usage patterns, seriously limiting the lateral impact of...
Open the catalog to page 4All Kontron catalogs and technical brochures
 K4021-U mSTX
5 Pages
 VX307H
6 Pages
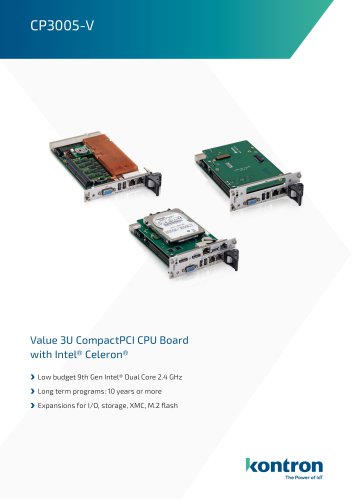 CP3005-V
7 Pages
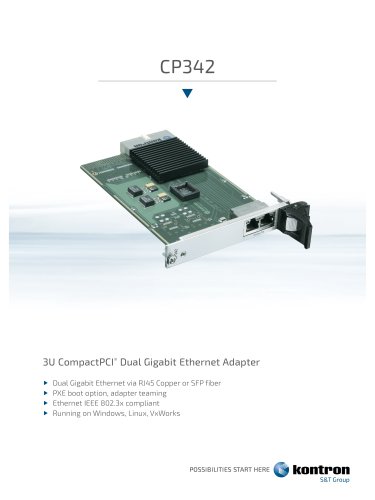 CP342
2 Pages
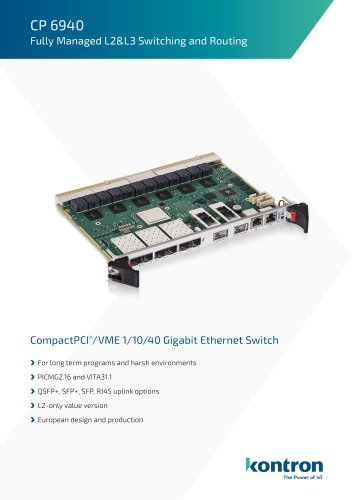 CP 6940
4 Pages
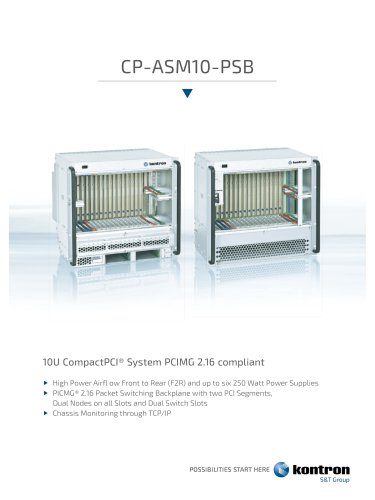 CP-ASM10-PSB
4 Pages
 CP-ASM6
3 Pages
 CP-XL SERIES
2 Pages
 CP-ASM1 LOW PROFILE RACK
2 Pages
 CP-ASM 3, CP-ASM4
4 Pages
 CP933
2 Pages
 CP-BP-KIT
2 Pages
 CP6007-SA
4 Pages
 CP6007-RA
4 Pages
 CP348
2 Pages
 VX3060-S2
4 Pages
 VX6940
4 Pages
 VX6090
4 Pages
 VX3106
2 Pages
 VX6124
5 Pages
 VX3058
4 Pages
 D3641-S μATX
5 Pages
 D3633-S mITX
5 Pages
 3.5”-SBC-TGL
4 Pages
 BL Pi-Tron CM3+
4 Pages
 BL i.MX6ULL/UL
4 Pages
 BL STM32 MP157
4 Pages
 BL i.MX8M Mini
4 Pages
 R4U8S/R4U8S
4 Pages
 VM6062
4 Pages
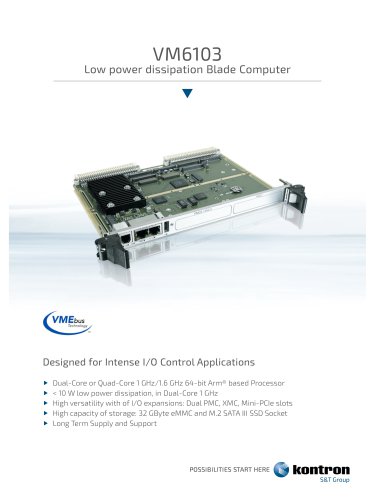 VM6103
5 Pages
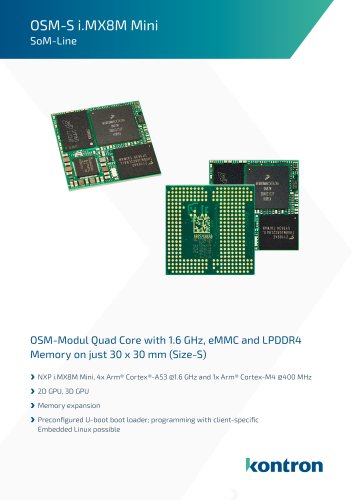 OSM-S i.MX8M Mini
4 Pages
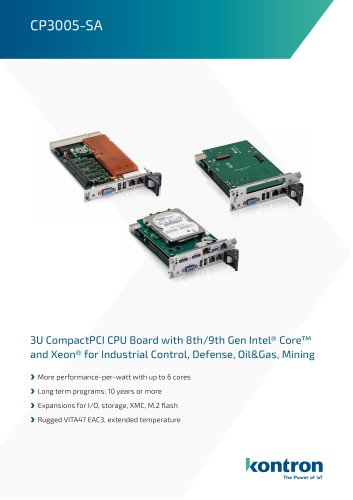 CP3005-SA
7 Pages
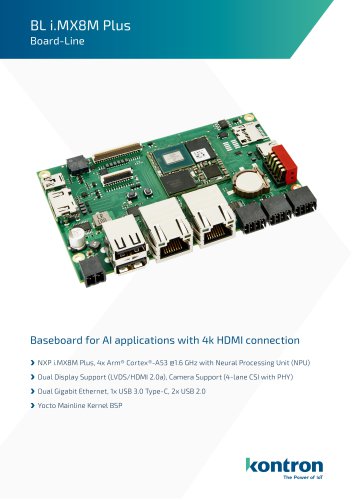 BL i.MX8M Plus
3 Pages
 3.5”-SBC-EKL
4 Pages
 BL Pi-Tron CM4
3 Pages
 BL Pi-Tron CM5
3 Pages
 BL i.MX93
3 Pages
 SMARTCASE™ S502
4 Pages
 VX307C
7 Pages
 VX6096
4 Pages
 VX6011-S
4 Pages
 VX3406
3 Pages
 VX3940
3 Pages
 VX3908
3 Pages
 OSM-S i.MX93
3 Pages
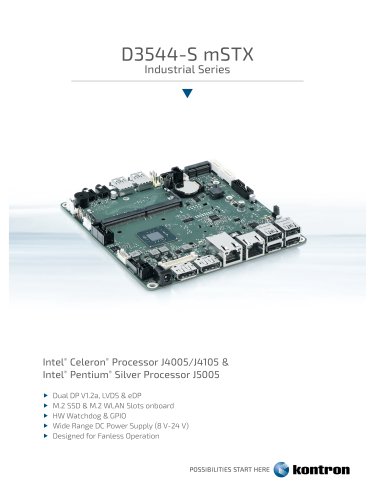 D3544-S mSTX
5 Pages
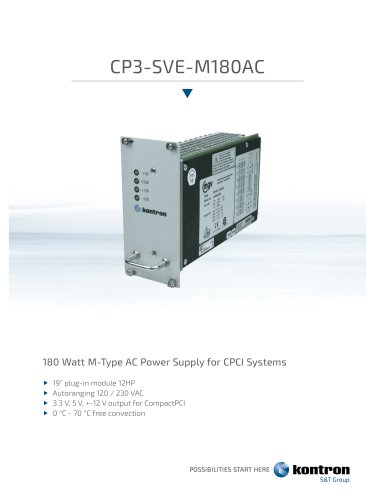 CP3-SVE-M180AC
6 Pages
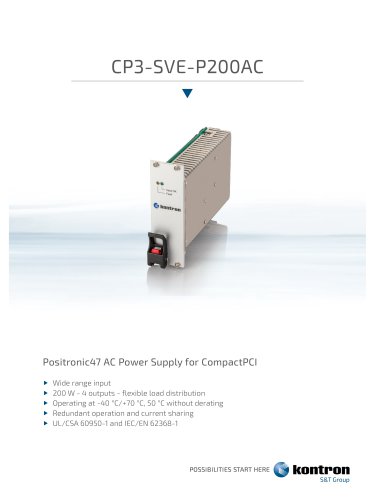 CP3-SVE-P200AC
6 Pages
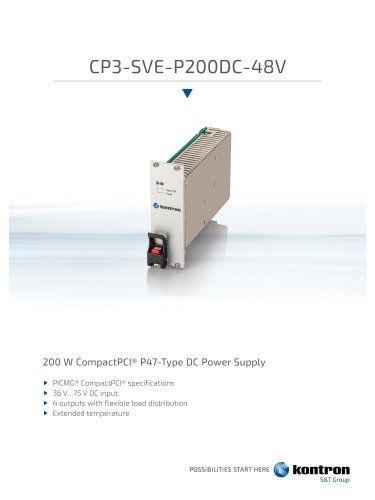 CP3-SVE-P200DC-48V
5 Pages
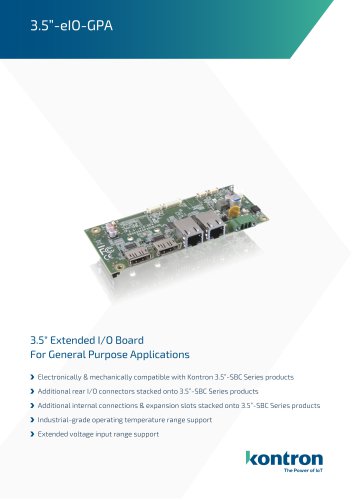 3.5”-eIO-GPA
4 Pages
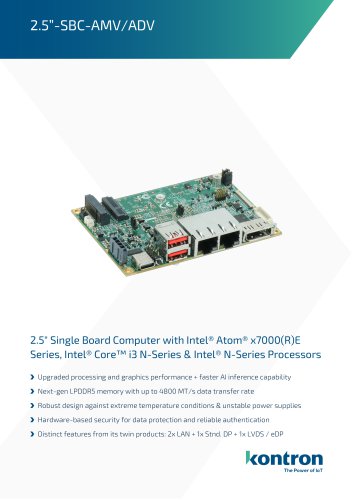 2.5”-SBC-AMV/ADV
4 Pages
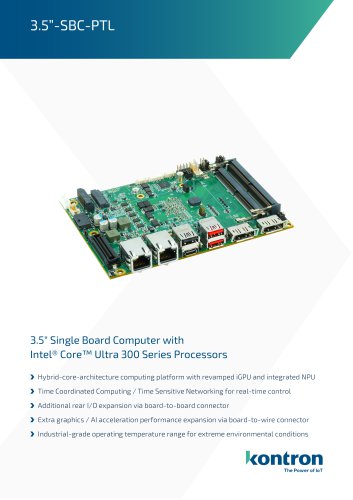 3.5”-SBC-PTL
4 Pages
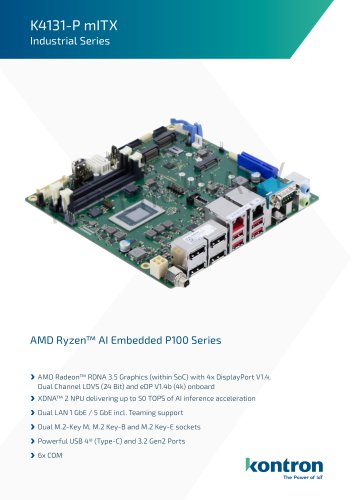 K4131-P mITX
5 Pages
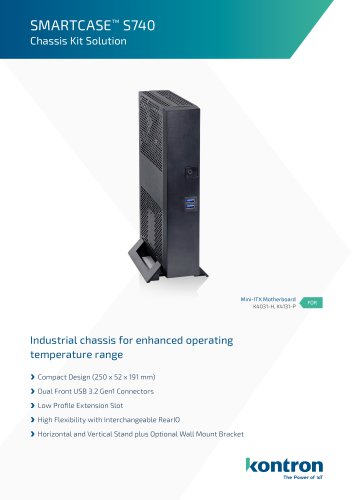 SMARTCASE™ S740
3 Pages
 OSM-S AM62L
3 Pages
 VX33211
6 Pages
 VX3124
6 Pages
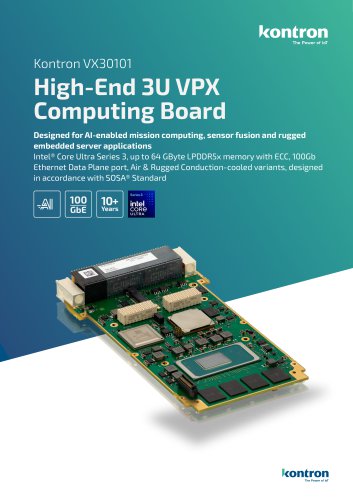 VX30101
6 Pages
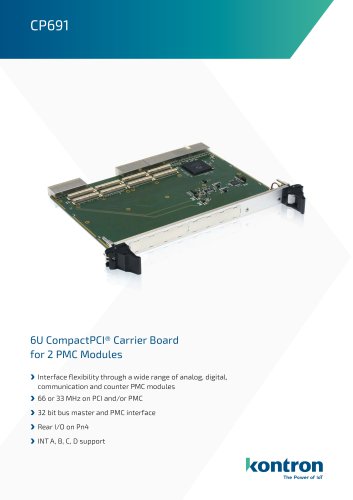 CP691
2 Pages
 MARATON Hazardous HE
3 Pages
 MARATON moderate HE
3 Pages
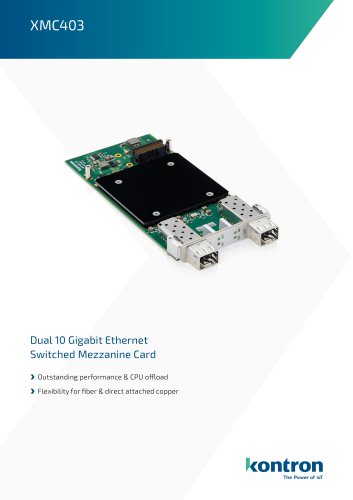 XMC403
3 Pages
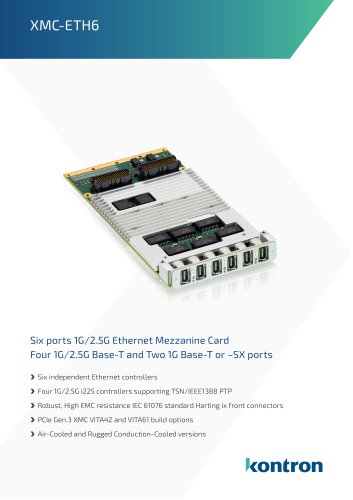 XMC-ETH6
3 Pages
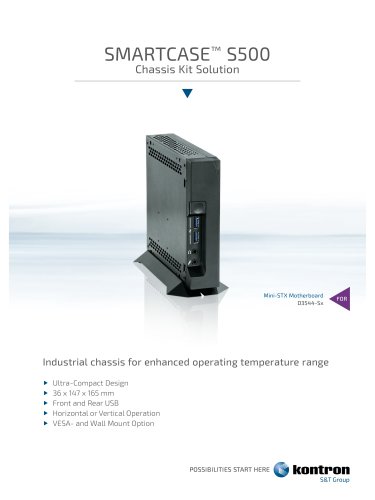 SMARTCASE™ S500
3 Pages
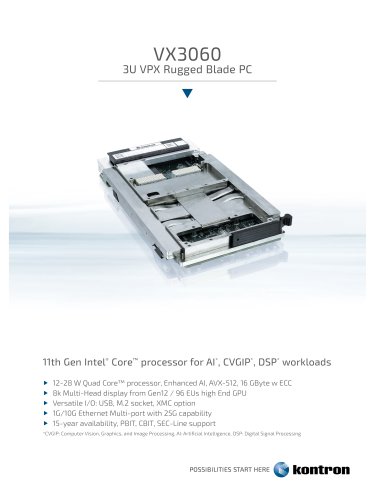 VX3060
4 Pages
 VPX1000
3 Pages
 VPX600
3 Pages
 VPX 360
6 Pages
 VPX340
5 Pages
 VPX336
5 Pages
 CMON-Line
4 Pages
 SEC-Line ELEMENTS
4 Pages
 kontron toolsuite
2 Pages
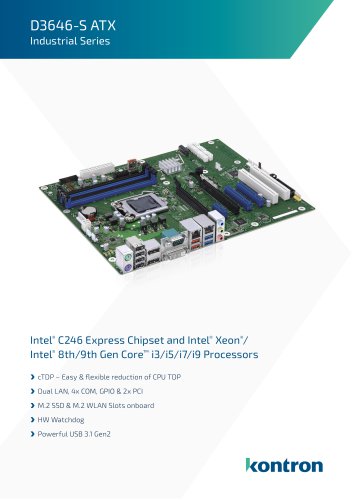 D3646-S ATX
5 Pages
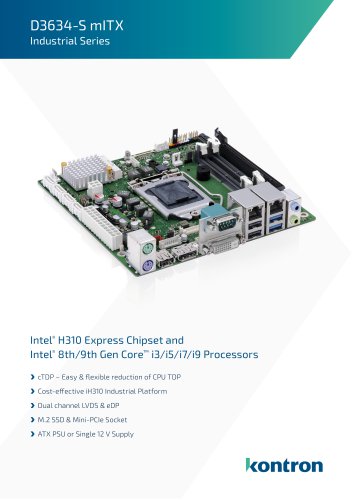 D3634-S mITX
5 Pages
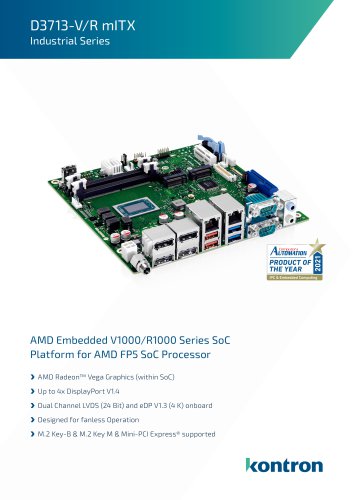 D3713-V/R mITX
5 Pages
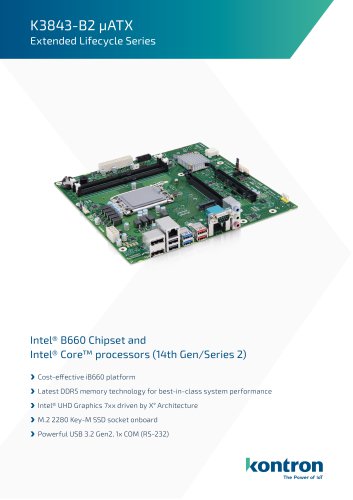 K3843-B2 µATX
5 Pages
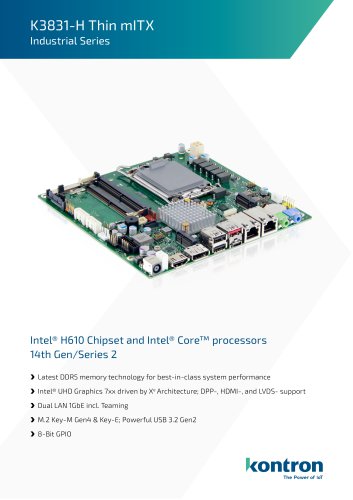 K3831-H Thin mITX
5 Pages
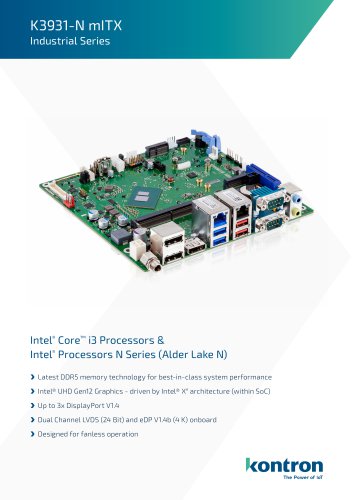 K3931-N mITX
5 Pages
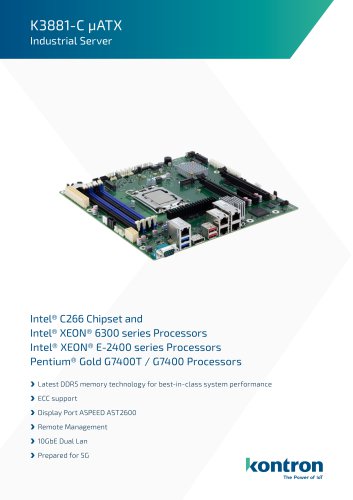 K3881-C µATX
5 Pages
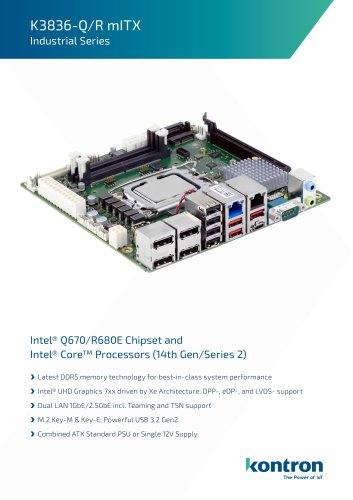 K3836-Q/R mITX
5 Pages
 K3882-C µATX
5 Pages
 K3833-Q mITX
4 Pages
 K4031-H mITX
5 Pages
 D3714-V/R mSTX
5 Pages
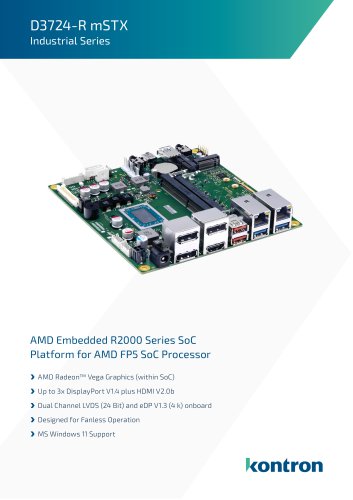 D3724-R mSTX
5 Pages
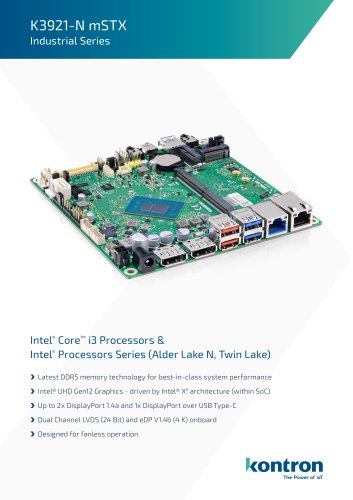 K3921-N mSTX
5 Pages
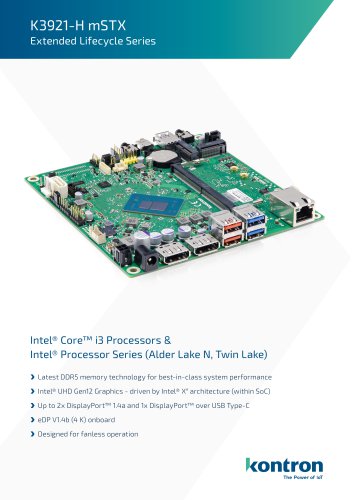 K3921-H mSTX
5 Pages
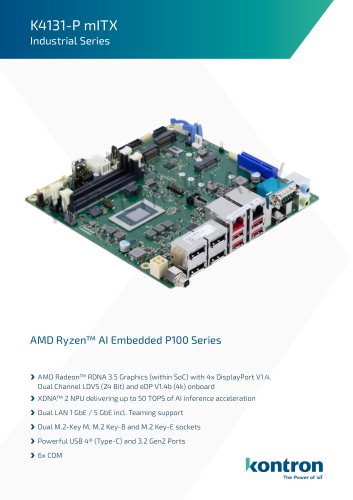 K4131-P mITX
5 Pages
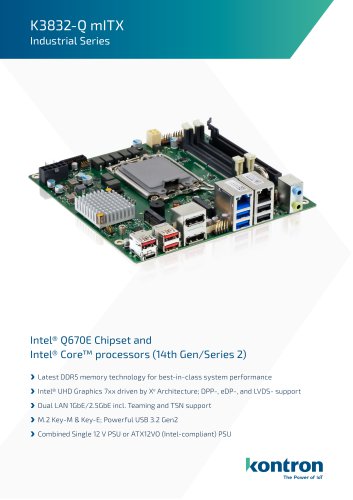 K3832-Q mITX
5 Pages
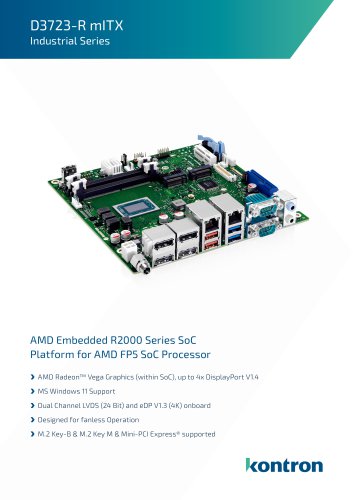 D3723-R mITX
5 Pages
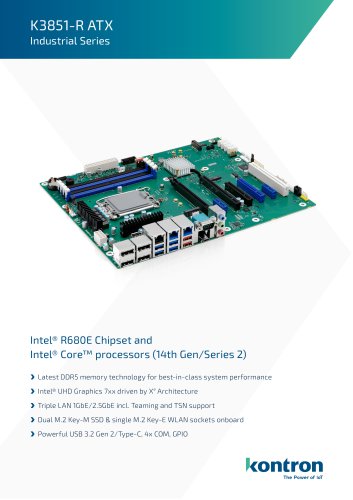 K3851-R ATX
5 Pages
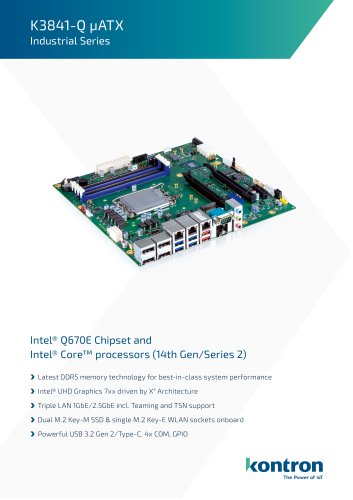 K3841-Q μATX
5 Pages
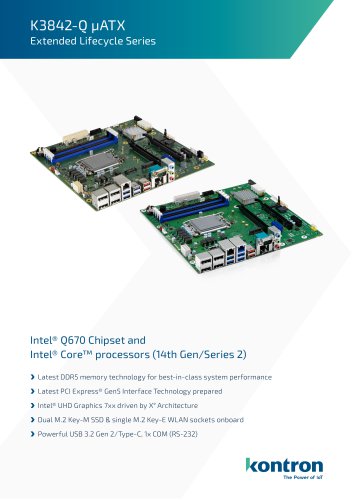 K3842-Q μATX
5 Pages
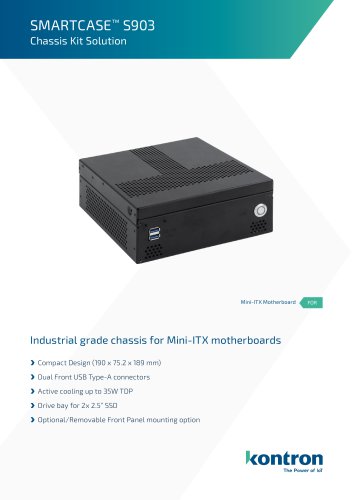 SMARTCASE S903
4 Pages
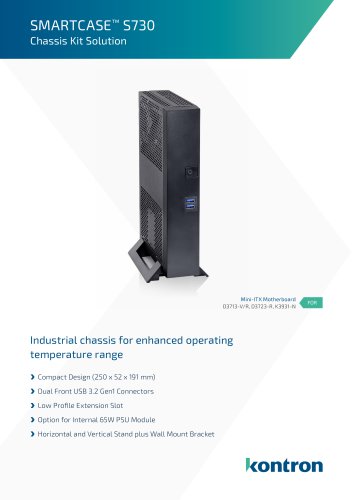 SMARTCASE S730
3 Pages
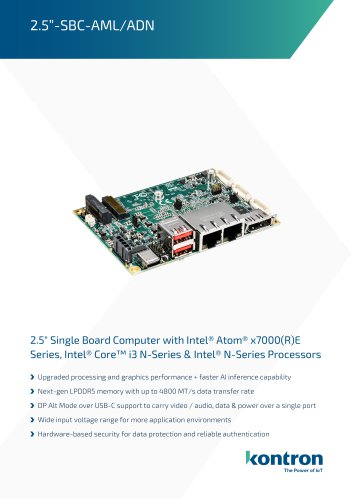 2.5"-SBC-AML/ADN
4 Pages
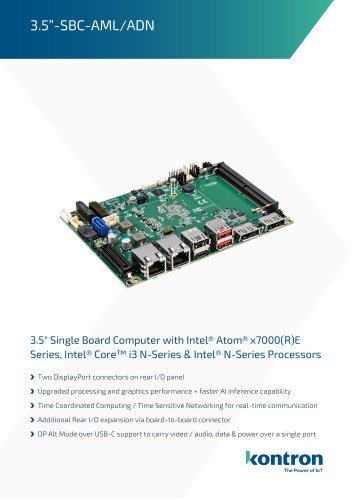 3.5"-SBC-AML/ADN
4 Pages
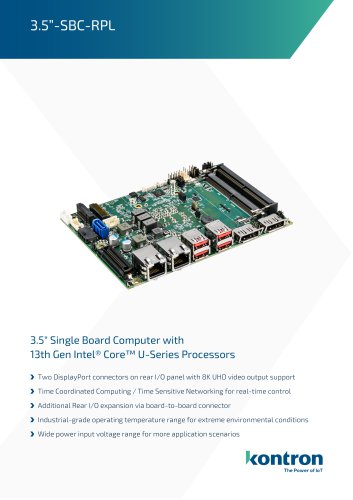 3.5"-SBC-RPL
4 Pages
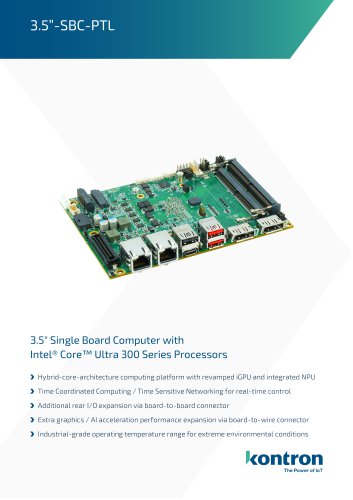 3.5"-SBC-PTL
4 Pages
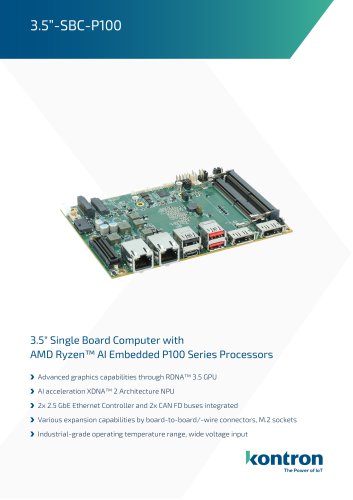 3.5"-SBC-P100
4 Pages
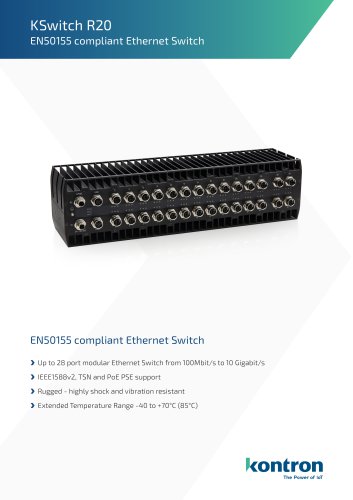 KSwitch R20
4 Pages
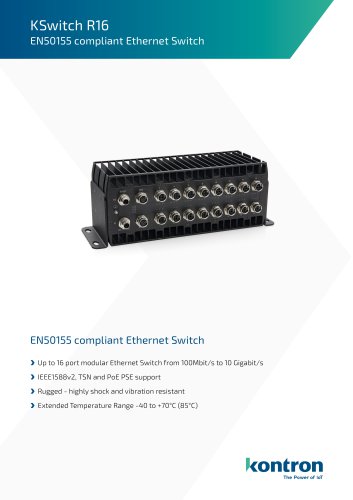 KSwitch R16
4 Pages
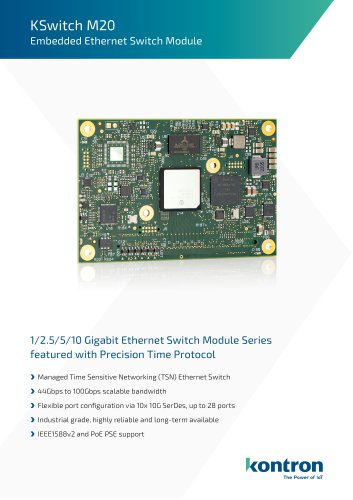 KSwitch M20
4 Pages
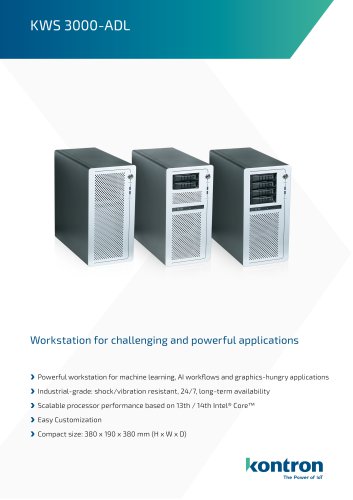 KWS 3000 ADL
4 Pages
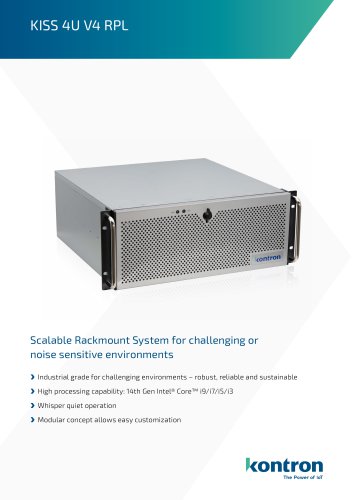 KISS 4U V4 RPL
2 Pages
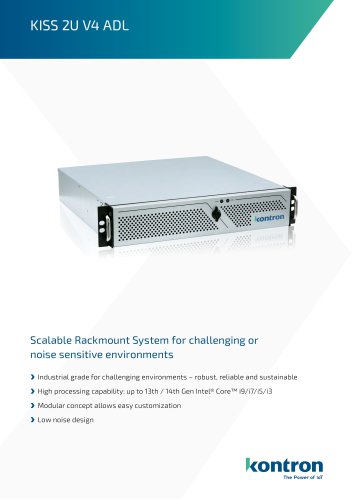 KISS 2U V4 ADL
2 Pages
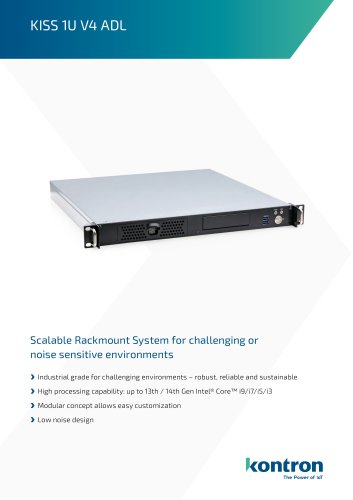 KISS 1U V4-ADL
3 Pages
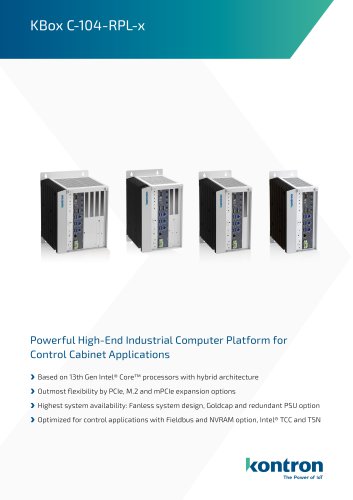 KBox C-104-RPL
4 Pages
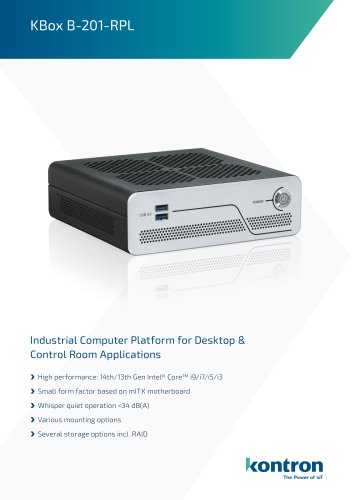 KBox B-201-RPL
4 Pages
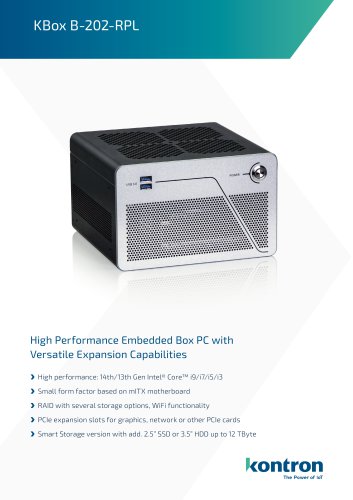 KBox B-202-RPL
4 Pages
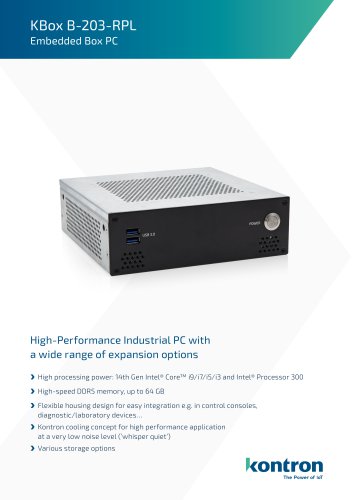 KBox B-203-RPL
4 Pages
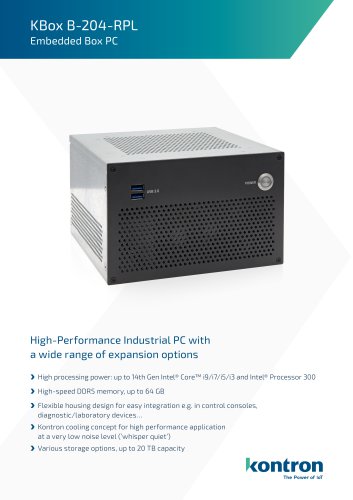 KBox B-204-RPL
4 Pages
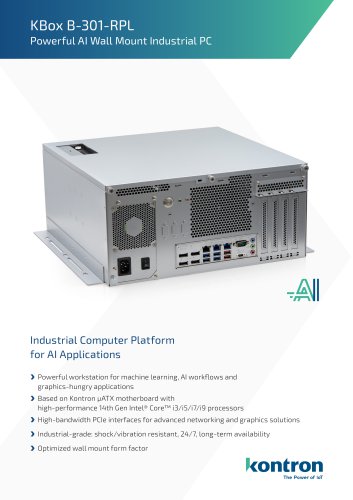 KBox B-301-RPL
3 Pages
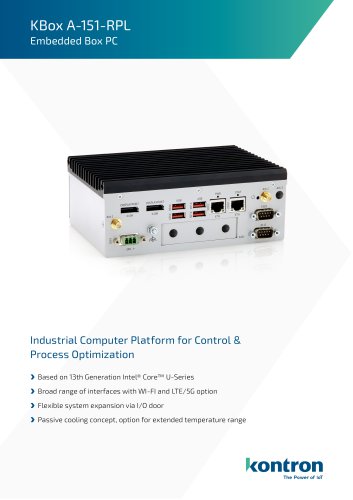 KBox A-151-RPL
5 Pages
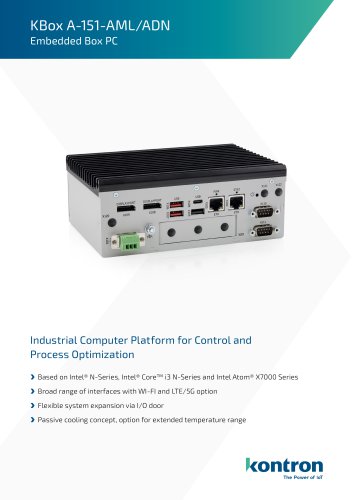 KBox A-151-AML/ADN
4 Pages
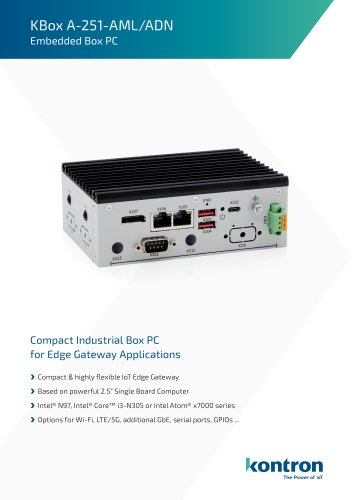 KBox A-151-AML/ADN
3 Pages
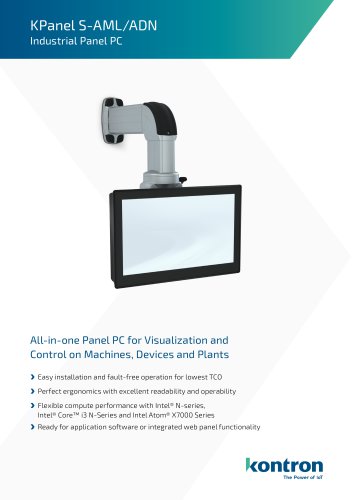 KPanel S-AML/ADN
4 Pages
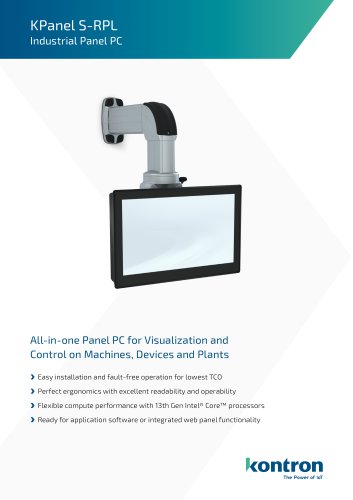 KPanel S-RPL
4 Pages
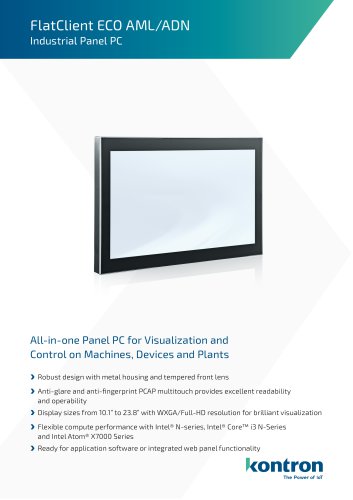 Flat Client ECO-AML/ADN
2 Pages
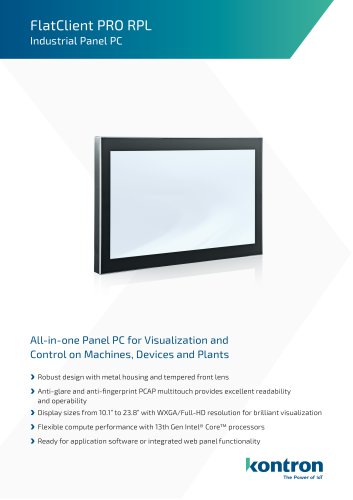 FlatClient PRO-RPL
2 Pages
 FlatView
3 Pages
 Open-frame
4 Pages
 Overview HMI Series
2 Pages
 STM32MP157
4 Pages
 web-panel
3 Pages
 CP
3 Pages
 RAILWAY EMBEDDED COMPUTING
2 Pages
 KONTRON TRANSPORTATION
1 Page
 VX305H-40G
4 Pages
 EvoTRAC-P101
2 Pages
 EvoTRAC-P201
2 Pages
 EvoTRAC™G103
2 Pages
 S2000 DEVELOPMENT PLATFORM
2 Pages
Archived catalogs
 SMARC-sXBT
2 Pages
 mitx-e38
4 Pages
 TRACe LoRa-MQTT
4 Pages
 IN-VEHICLE SERVER
2 Pages
 vehicle-server-cellular-ds
2 Pages
 Qseven-Q7AMX8X
2 Pages
 Kbox
2 Pages
 COMe-cBW6
2 Pages
 END-TO-END IOT SOLUTIONS
16 Pages
 pITX-E38
4 Pages
 KTAM3874/pITX
2 Pages
 vx3030-datasheet-08-14
4 Pages
 vmpx_accessories
2 Pages
 vmp3_datasheet
4 Pages
 datasheet_cp-hdd-s-kit
2 Pages
 ds_cp371_052011
2 Pages
 MARS Concept Brochure
6 Pages
 VME Product Catalog
6 Pages
 CompactPCI Product Brochure
8 Pages
 VPX products & Solutions
9 Pages
 COM Express® Concept Folder
6 Pages
 Fanless Box PCs - CB Series
3 Pages
 Product Highlights
4 Pages
 Motherboards & SBCs
11 Pages
 Kontron Services
2 Pages
 Medical Catalog
8 Pages
 Commercial Avionics
2 Pages
 Embedded Boards
31 Pages
 Open Communication Platforms
32 Pages
 Military Defense
8 Pages
 Kontron Highlight Folder
16 Pages
 Box PC
2 Pages
 Transportation Folder
11 Pages
 MicroTCA
2 Pages
 Industrial Automation Catalog
11 Pages
 hmi_global_2012
8 Pages
 m2m_platforms
2 Pages


- Kontron power supply
- Kontron DC power supply
- Kontron panel PC
- Kontron industrial panel PC
- Kontron panel PC with touch screen
- AC/DC power supply
- Touch monitor
- Fanless panel PC
- Ethernet switch
- LCD screen
- Kontron LCD panel PC
- Industrial monitor
- Management software solution
- Kontron Intel® Core™ PC
- HDMI monitor
- Kontron industrial PC
- Kontron fanless PC
- Kontron IP65 panel PC
- Kontron Intel® Core™ panel PC
- HDMI PC