
- Catalogs
- Juniper Networks
- SRX1500 FIREWALL DATASHEET


SRX1500 FIREWALL DATASHEET
SRX1500 FIREWALL DATASHEET
The Juniper Networks SRX1500 is a high-performance next-generation firewall tailored for distributed enterprises. It combines security, threat detection, and mitigation with carrier-class routing and switching, supporting cloud-enabled networks for scalable and secure connectivity.
Architecture
The SRX1500 is equipped with a security flow accelerator and an x86-based security compute engine, enhancing performance within a compact 1U form factor. It is designed for 10GbE environments, integrating security services with networking functions.
Key Features
The SRX1500 offers application visibility and control, advanced threat protection via Juniper ATP Cloud, AI-Predictive Threat Prevention, high-performance IPsec VPN, and integrated routing, switching, and security.
Security and Threat Management
It provides comprehensive application security and threat defenses, integrating with Juniper's Advanced Threat Prevention Cloud for adaptive protection and utilizing AI for accurate threat detection.
Management and Automation
Centralized management is facilitated by Juniper Security Director Cloud, ensuring consistent security policies. The SRX1500 supports Zero Touch Deployment and automation for efficient operations.
Juniper Secure Edge
Secure Edge delivers full-stack SSE capabilities, including FWaaS and ZTNA, ensuring secure application access with a unified policy framework.
Specifications
- Firewall Services: Stateful inspection, DDoS protection, SSL Inspection
- VPN Features: IPsec, SSL VPN, IKE encryption and authentication
- High Availability: VRRP, active/passive and active/active clustering
- Routing Protocols: IPv4/IPv6, OSPF, BGP, EVPN-VXLAN
- QoS Features: Traffic classification, policing, and shaping
- Switching Features: Layer 2 forwarding, VLAN support, link aggregation
The document highlights network protocols and management tools such as BFD, TWAMP, IEEE 802.3ah LFM, and IEEE 802.1ag CFM, crucial for network fault detection and management.
Advanced Routing Services
Advanced routing services include packet mode, MPLS (RSVP, LDP), circuit cross-connect, L2/L2 MPLS VPN, pseudo-wires, VPLS, NG-MVPN, MPLS traffic engineering, and MPLS fast reroute, enhancing routing capabilities and efficiency.
Management, Automation, Logging, and Reporting
Management tools include SSH, Telnet, SNMP, Juniper CLI and Web UI, and Security Director Cloud. Automation is supported through Python and Junos OS scripts. Reporting includes application and bandwidth usage, with tools for debugging and troubleshooting.
Hardware Specifications
The SRX1500 includes 16x1GbE and 4x10GbE onboard ports, 12x1GbE RJ-45 ports, 4x1GbE SFP transceiver ports, 4x10GbE SFP+ ports, and 1x1GbE out-of-band management port. It features a 1U form factor, 16 GB RAM, and supports redundant power supply.
Performance and Scale
Performance metrics include firewall throughput of 4.5 Gbps (IMIX) and 9.0 Gbps (1,518 B), IPsec VPN throughput of 1.0 Gbps (IMIX) and 4.0 Gbps (1400 B), and application security performance of 7.5 Gbps. It supports a route table size of 2 million (RIB) and 1 million (FIB) for IPv4, with up to 2,000,000 concurrent sessions.
Juniper Networks Services and Support
Juniper Networks offers services to enhance network performance, reduce costs, and minimize risks, emphasizing operational efficiency and reliability.
Ordering Information
For purchasing and licensing, refer to Juniper's How to Buy page.
About Juniper Networks
Juniper Networks focuses on AI-Native Networking to deliver secure user experiences across various network environments. More information is available on their website and social media.
Catalog excerpts
SRX1500 FIREWALL DATASHEET Next-Generation Firewall For The Distributed Enterprise Product Description Product Overview The SRX1500 is a nextgeneration firewall and security services gateway offering outstanding protection, performance, scalability, availability, and security service integration. Designed for port density, a high-performance security services architecture, and seamless integration of networking and security in a single platform, the SRX1500 is best suited for client protection in enterprise campuses, regional headquarters, or cloud-based security solutions with a focus on application visibility and control, intrusion prevention, and advanced threat prevention. The SRX1500, powered by Junos OS, is the industry-leading operating system that keeps the world's largest and most mission-critical enterprise networks secure. The Juniper Networks® SRX1500 is a high-performance next-generation firewall and security services gateway that protects mission-critical networks at campuses, regional headquarters, and large branch offices. The SRX1500 provides best-in-class security, threat detection, and mitigation capabilities, integrating carrier-class routing and feature-rich switching in a single platform. The SRX1500 delivers a next-generation security solution that supports the changing needs of cloud-enabled enterprise networks. Whether rolling out new services in an enterprise campus, connecting to the cloud, complying with industry standards, or achieving operational efficiency, the SRX1500 helps organizations realize their business objectives while providing scalable, easy-to-manage, secure connectivity and advanced threat detection and mitigation capabilities. The SRX1500 protects critical corporate assets as a next-generation firewall, acts as an enforcement point for cloud-based security solutions, and provides application visibility and control to improve the user and application experience. Hardware and software architectures on the SRX1500 provide significant performance improvements to a small 1 U form factor. The key to the SRX1500 hardware is the security flow accelerator and a robust x86-based security compute engine for advanced security services like application visibility, intrusion prevention, and threat mitigation capabilities. The SRX1500 software architecture leverages these hardware components and virtualization to deliver high-speed firewall performance, application visibility, and intrusion prevention while lowering the total cost of ownership (TCO). The SRX1500 is purpose-built to protect 10GbE network environments, consolidating multiple security services and networking functions in a highly available appliance. SRX1500 Highlights The SRX1500 fully complements next-generation firewall capabilities that help secure your network with an integrated solution that combines best-in-class application, content, and threat classification with SD-WAN, local switching, and easy policy management. Advanced application identification and classification enable greater visibility, enforcement, control, and protection over the network as they are tied to users regardless of location or device. It provides a detailed analysis of application volume and usage and fine-grained application control policies to allow or deny traffic based on dynamic application names or group names, and prioritization of traffic based on application information and context to reduce complexity across traditional, cloud, and hybrid IT networks. By combining perimeter defenses with segmentation, the SRX1500 firewall provides a comprehensive suite of application security, threat defenses, and intelligence services to protect networks from content-borne threats. Integrated threat intelligence via Juniper Networks Advanced Threat Prevention (ATP) Cloud offers adaptive threat protection against command and control (C&C) solutions that leverage automated protection. This
Open the catalog to page 1
integration helps detect and enforce against known exploits, spyware, malware, and zero-day threats with an extremely high degree of accuracy using advanced AI techniques developed in conjunction with Juniper Threat Labs. The SRX1500 enables agile SecOps through automation capabilities that support Zero Touch Deployment, Python scripts for orchestration, and event scripting for operational management. The SRX1500 delivers fully automated SD-WAN to both enterprises and service providers. A Zero Touch Provisioning (ZTP) capability simplifies branch network connectivity for initial deployment and...
Open the catalog to page 2
Features and Benefits Business Requirement High performance High-performance firewall SRX1500 Advantages • Best suited for enterprise large branch and campus deployments • Addresses future needs for scale and feature capacity High-quality end user experience Application visibility and control • Continuous application updates provided by Juniper Threat Labs • Controls and prioritizes traffic based on application and user role • Inspects and detects applications inside the SSL-encrypted traffic Threat protection IPS, antivirus, antispam, enhanced web filtering, Juniper Advanced Threat Prevention...
Open the catalog to page 3
• Authentication: Pre-shared key and public key infrastructure (PKI) (X.509) • IPsec (Internet Protocol Security): Authentication Header (AH)/ Encapsulating Security Payload (ESP) protocol • IPsec Authentication Algorithms: hmac-md5, hmac-sha-196 • IPsec Encryption Algorithms: Prime, DES-CBC, 3DES-CBC, AEC-CBC, AES-GCM, SuiteB • Perfect forward secrecy, anti-reply • Internet Key Exchange: IKEv1, IKEv2 • Monitoring: Standard-based dead peer detection (DPD) support, VPN monitoring • VPNs GRE, IP-in-IP, and MPLS High Availability Features • Virtual Router Redundancy Protocol (VRRP) • Stateful high...
Open the catalog to page 4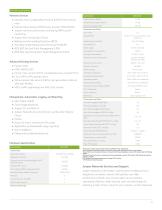
Network Services • Dynamic Host Configuration Protocol (DHCP) client/server/ relay • Domain Name System (DNS) proxy, dynamic DNS (DDNS) Power supply AC/DC (external) Average power consumption Average heat dissipation Packet mode MPLS (RSVP, LDP) Circuit cross-connect (CCC), translational cross-connect (TCC) L2/L2 MPLS VPN, pseudo-wires Virtual private LAN service (VPLS), next-generation multicast Maximum current consumption Maximum inrush current Acoustic noise level Operating temperature Nonoperating temperature Operating humidity Nonoperating humidity Meantime between failures (MTBF) RoHS compliance...
Open the catalog to page 5All Juniper Networks catalogs and technical brochures
 EX2300-C COMPACT ETHERNET SWITCH
10 Pages
 EX3400 ETHERNET SWITCH
13 Pages
 EX4300 LINE OF ETHERNET SWITCHES
17 Pages
 EX4600 ETHERNET SWITCH
13 Pages
 EX4650 Ethernet Switch
13 Pages
 EX9200 Ethernet Switch
15 Pages
 EX9250 Ethernet Switch
12 Pages
 EX2300 ETHERNET SWITCH
12 Pages
 QFX5200 SWITCH
13 Pages
 QFX5210 SWITCH
9 Pages
 ISG Series
11 Pages


Archived catalogs
 EX4300 Ethernet Switch
12 Pages
 WLA Series Antenna Matrix
2 Pages
 QFX3100 QFabric Director
4 Pages
 EX Series Ethernet Switches
20 Pages
 QFX3500 Switch
12 Pages
 QFX3600 Switch
12 Pages
 QFabric System
12 Pages
 QFX5100 Ethernet Switch
12 Pages
 Unified Access Control
12 Pages
 DDoS Secure
4 Pages
 LN2600 Rugged Secure Router
6 Pages
 1100018
6 Pages
 1000195
6 Pages
 1000300
4 Pages
 backgrounder
4 Pages
 VXA Series
4 Pages
 SRX1400 Services Gateway
8 Pages
 Security Services Gateways
8 Pages
 T Series Core Routers
8 Pages
 JCS1200 Control System
6 Pages
 J Series Services Routers
16 Pages
 BX7000 Multi-Access Gateway
4 Pages
 EX4550 Ethernet Switch
12 Pages
 JSA Series Secure Analytics
12 Pages
 LN1000 Mobile Secure Router
6 Pages
 JSA7500
8 Pages
 AP150W
2 Pages
 AP245X
2 Pages
 AP250
2 Pages
 AP550
2 Pages


- Ethernet switch
- Automation software solution
- Management software solution
- Analysis software solution
- Process software
- Computer-aided design software
- Cloud-based software
- Managed switch
- Control software
- Gigabit Ethernet ethernet switch
- RJ45 network switch
- Design software solution
- Monitoring software solution
- Redundant network switch
- PoE network switch
- Visualization software solution
- Quality software
- Layer 2 network switch
- Simulation software solution